u/border_dad
· 5h
Uninstall it. A Russian Zoom is not a branding joke.
As an Amazon Associate I earn from qualifying purchases.
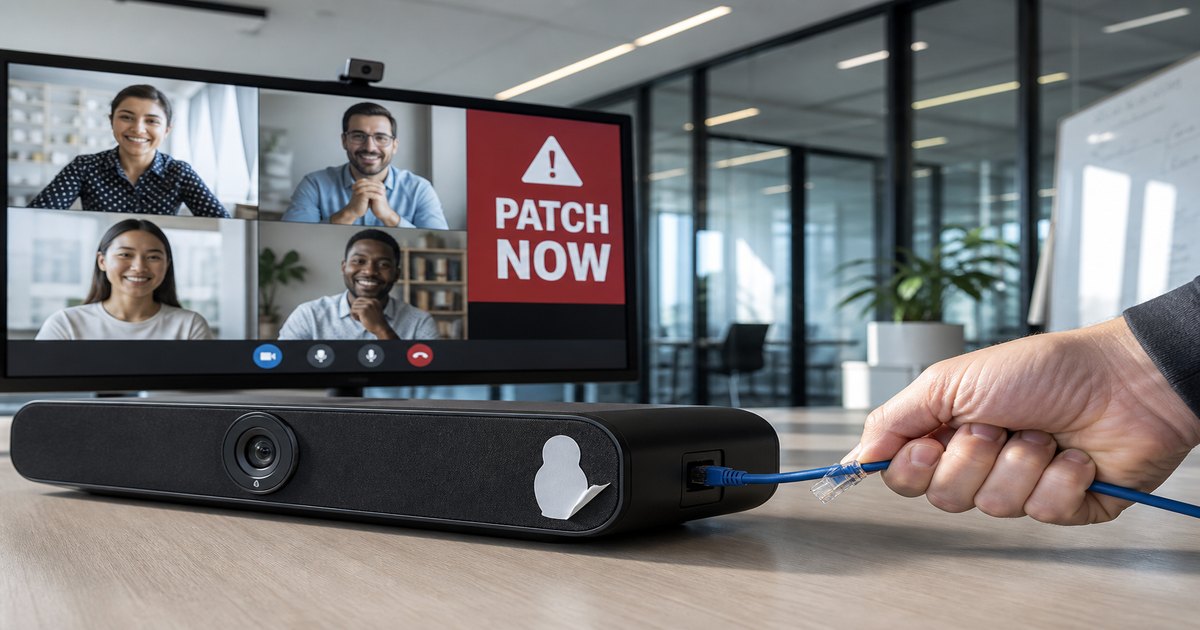
CISA told operators to patch TrueConf, the Russian Zoom. If it is still on the box, the meeting is the vulnerability.
A county IT man still inherits a conference box because a contractor liked the price. He does not inherit the right to keep a Moscow vendor after CISA clears its throat.
That is the gap. The patch note is polite. The product is a Russian pipe. Hacktivists already have a key. So can a service that is not a hacktivist.
Ask the board that approved the license: if Ukraine can walk in, why is the software still on the VLAN?
Uninstall it. A Russian Zoom is not a branding joke.
I would not put a Soviet radio in a TOC. Do not put this in a clinic.
CISA said patch. Agencies should say remove. Write the directive.
Allied networks should keep a deny list, not a discount list.
Procurement that bought this should have to sign the incident form.
I join a standup on a laptop. I do not want Moscow in the codec.
If Ukraine is already in the hole, so is everyone else. Pull the plug.
Same file as Volt Typhoon. Foreign software is a weapon when it wants to be.
The Register named CISA and TrueConf. Keep both in the ticket.
Patch today. Ban tomorrow. Inventory every Russian app this week.
 NEW